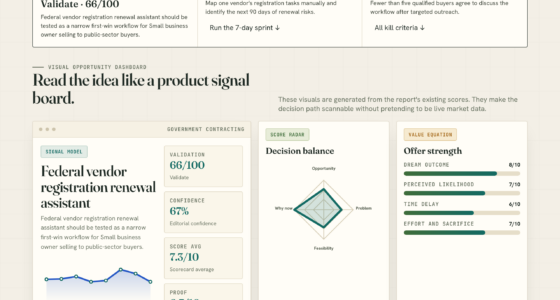
📊 Full opportunity report: CMMC Compliance Automation For The Defense Industrial Base on IdeaNavigator AI — validation score, market gap, and execution plan.

Get business pricing on office and shipping supplies
- Business-only prices and quantity discounts
- Tax-exempt purchasing
- Multiple users, one account, clear invoices
TL;DR
A proposed software opportunity would help small and midsize Defense Industrial Base contractors prepare for CMMC Level 2 by organizing assessments, evidence and required documents. The market case rests on a phased rollout that began in November 2025, but the product concept and demand figures have not been independently validated here.
IdeaNavigator AI has proposed a software workflow to help small and midsize U.S. defense contractors prepare for CMMC Level 2, by collecting assessment answers and generating draft compliance documents. The concept responds to the phased introduction of CMMC contract requirements, but it is a product opportunity—not an announcement that a tool has launched or that contractors have adopted it.
The proposed tool is aimed at contractors and subcontractors handling Federal Contract Information (FCI) or Controlled Unclassified Information (CUI), particularly organizations without a dedicated cybersecurity compliance team. Its initial workflow would guide a company through a NIST SP 800-171 self-assessment, map responses to the 110 security requirements, and produce draft System Security Plan (SSP) and Plan of Action and Milestones (POA&M) documents. It would also calculate a Supplier Performance Risk System (SPRS) score and provide a prioritized remediation roadmap with evidence checklists.
The proposal recommends starting with structured assessments and document generation rather than building continuous monitoring software at the outset. The intended benefit is to help a single compliance lead organize readiness materials more quickly. However, generated documents would still need to reflect the contractor’s actual systems and practices; the proposal does not establish that automation alone can satisfy an assessment or certify compliance.
IdeaNavigator AI describes a possible annual subscription priced at roughly $5,000 to $25,000, tiered by company size or control scope, with potential paid services such as remediation guidance and evidence collection. These are suggested commercial assumptions, not announced prices or evidence of customer commitments. The proposed validation plan is to recruit 15 to 25 contractors for guided assessments and measure completion, interest in generated documents and willingness to pay for a pilot.
Pressure on Smaller Contractors
CMMC readiness can affect whether a contractor remains eligible for certain Department of Defense work once relevant requirements appear in solicitations. For smaller firms, the work involves more than filling out a questionnaire: they must document how security requirements are met, identify gaps, preserve evidence and address deficiencies. A company with limited internal security capacity may have to divide this effort among operations, IT and contract staff.
The supplied proposal estimates that a first Level 2 compliance cycle can cost $75,000 to $300,000 or more and take 12 to 18 months. Those figures are presented as typical estimates, not independently verified costs for every contractor. If accurate for a particular firm, the time and expense make early planning relevant to businesses that depend on defense contracts. Software that improves organization could help, but it would not remove the need for technical remediation or an assessment where one is required.
Automation also raises a practical distinction: producing a complete-looking SSP is not the same as operating the controls described in it. Contractors would need to check generated content against their environment and maintain supporting evidence. The value of a tool would depend on whether it reduces administrative work without creating misleading or outdated compliance records.
Products Worth Considering

LG UltraGear 27-Inch QHD OLED Gaming Monitor, 240Hz, 0.03ms, G-SYNC Compatible, FreeSync Premium Pro, HDMI 2.1

Samsung 27-inch Odyssey OLED G6 QD-OLED QHD Gaming Monitor

Samsung 27-Inch Odyssey QD-OLED G8 4K 240Hz Gaming Monitor
As an affiliate, we earn on qualifying purchases.
CMMC Rollout and Requirements
The supplied material says the CMMC DFARS final rule took effect on November 10, 2025, beginning a three-year phased rollout. It describes Level 1 and Level 2 self-assessment and third-party assessment requirements as entering selected solicitations during Phase 1, with requirements becoming broadly mandatory by November 2028. Contractors should check the clauses in each solicitation and applicable government guidance; the rollout does not mean every contract has the same requirement on the same date.
Level 2 is tied to protecting CUI and draws on NIST SP 800-171. The proposed workflow treats the assessment, SSP, POA&M, SPRS score and evidence organization as a connected readiness process. The material estimates that more than 118,000 companies may need Level 2 certification and that about 68% of affected entities are small businesses. These are estimates supplied with the proposal, rather than independently confirmed counts in this report.
Product and Demand Still Unproven
No product launch, customer results, completed pilot, or independent evaluation is described. It is also unclear whether the estimated number of companies needing Level 2 certification, the small-business share, and the stated cost and timeline reflect a defined study or a particular set of contractors. They should be treated as planning estimates, not settled measurements.
The proposed price range and add-on revenue streams are likewise assumptions. The material does not identify a vendor, demonstrate that automated SSP or POA&M drafts meet assessor expectations, or explain how the tool would handle different system boundaries, subcontractor relationships and evidence quality. Nor does it specify how generated records would be kept current as a contractor changes its systems.
Contractors should also distinguish readiness assistance from certification. A software workspace can help organize information, but the proposal does not claim that using one guarantees a passing assessment, preserves contract eligibility, or substitutes for required independent assessment.
Testing the Readiness Workflow
The next proposed step is a small validation effort with 15 to 25 contractors, recruited through industry groups, APEX Accelerators and CMMC forums. The team would offer guided self-assessments and examine how many participants complete them, whether they want draft SSPs and POA&Ms, and whether any will commit to a paid pilot. A landing page offering a free readiness score and SSP draft is another suggested way to gauge qualified interest.
Those tests could establish whether contractors find the workflow useful and whether they will pay for it; they would not, on their own, prove that the software produces assessment-ready documentation across the market. For contractors, the near-term practical step is to review solicitation language and applicable CMMC requirements, identify their information systems and data scope, and plan remediation early enough to meet the requirements tied to the work they pursue. No pilot results or product timetable have been reported.
Source: IdeaNavigator AI
Key Questions
Has a CMMC automation product been launched?
The material outlines a proposed product and validation plan. It does not report a launch, completed pilot or customers.
What would the proposed tool do?
It would guide a NIST SP 800-171 self-assessment, map responses to 110 requirements, and generate draft SSP and POA&M documents, an SPRS score and a remediation roadmap.
Does using automation certify a contractor?
No. The proposal describes readiness and documentation support, not certification. Contractors remain responsible for accurate records, implemented security practices and any assessment their contract requires.
When do CMMC requirements apply?
The supplied material describes a phased rollout beginning November 10, 2025, with requirements appearing in selected solicitations and becoming broadly mandatory by November 2028. Applicability depends on the contract and its solicitation terms.
Have the proposed costs and market estimates been verified?
No independent verification is provided here. The $75,000 to $300,000-plus cost range, 12-to-18-month timeline and market counts should be read as estimates attributed to the proposal.
Source: IdeaNavigator AI